

Before you start
In order to understand this guide correctly you must be familiar with some Auth0 Fine-Grained Authorization (FGA) concepts and know how to develop the things that we will list below.What you will be modeling
Slack is a messaging app for businesses that connects people to the information they need. By bringing people together to work as one unified team, Slack transforms the way organizations communicate. (Source: What is Slack?) In this tutorial, you will build a subset of the Slack permission model (detailed below) in Auth0 Fine-Grained Authorization (FGA), using some scenarios to validate the model.As reference, you can refer to Slack’s publicly available docs:
Note: For brevity, this tutorial will not model all of Slack’s permissions. Instead, it will focus on modeling the scenarios outlined below.
Requirements
This tutorial will focus on the following sections (this is a partial list of Slack’s roles): Workspace Roles:- Guest: This type of user is limited in their ability to use Slack, and is only permitted to see one or multiple delegated channels.
- Member: This is the base type of user that does not have any particular administrative abilities, but has basic access to the organization’s Slack workspaces. When an administrative change needs to be made, these users need the support of admins and owners to make the changes.
- Legacy Admin: This type of user is the basic administrator of any organization, and can make a wide variety of administrative changes across Slack, such as renaming channels, archiving channels, setting up preferences and policies, inviting new users, and installing applications. Users with this role perform the majority of administrative tasks across a team.
- Channels Admin: This type of user has the permission to archive channels, rename channels, create private channels, and convert public channels into private channels.
- Visibility:
- Public: Visible to all members and open to join
- Private: Visible to admins and invited members
- Posting Permissions:
- Open: Anyone can post
- Limited: Only allowed members can post
Defined scenarios
Use the following scenarios to be able to validate whether the model of the requirements is correct. There will be the following users:- Amy
- Bob
- Catherine
- David
- Emily
- You will assume there is a Slack workspace called Sandcastle
- Amy is a legacy admin of the Sandcastle workspace
- Bob is a member of the Sandcastle workspace with a channels admin role (Read more about system roles at Slack here)
- Catherine and Emily are normal members of the Sandcastle workspace, they can view all public channels, as well as channels they have been invited to
- David is a guest user with only view and write access to #proj-marketing-campaign, one of the public channels in the Sandcastle workspace
- Bob and Emily are in a private channel #marketing-internal in the Sandcastle workspace which only they can view and post to
- All members of the Sandcastle workspace can view the general channel, but only Amy and Emily can post to it
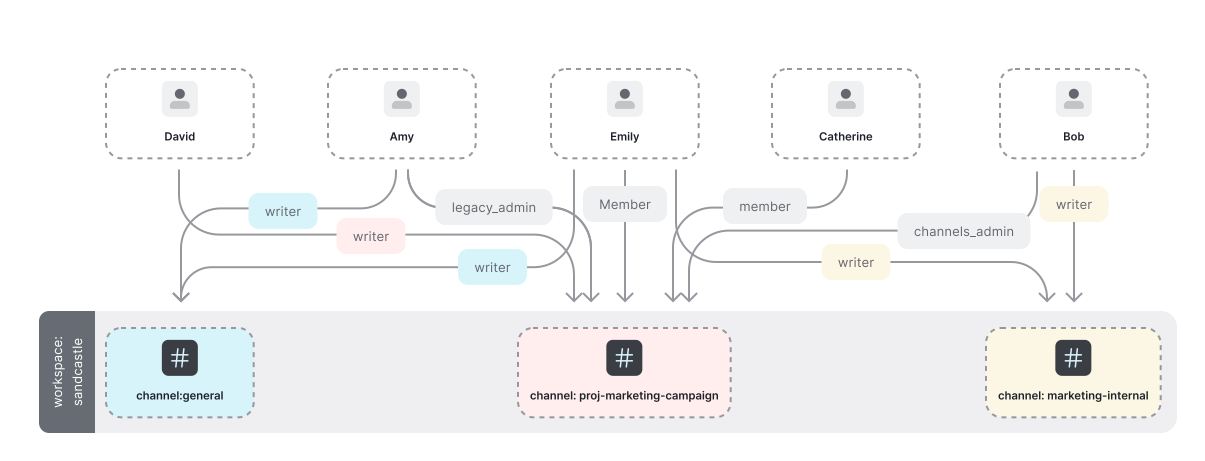
Modeling workspaces & channels
The goal by the end of this post is to ask Auth0 Fine-Grained Authorization (FGA): Does person X have permission to perform action Y on channel Z? In response, you want to either get a confirmation that person X can indeed do that, or a rejection that they cannot. E.g. does David have access to view #general? The Auth0 Fine-Grained Authorization (FGA) is based on Zanzibar, a Relation Based Access Control system. This means it relies on objects and user relations to perform authorization checks. Setting aside the permissions, you will start with the roles and learn how to express the requirements in terms of relations you can feed into Auth0 FGA. The requirements stated:- Amy is a legacy admin of the Sandcastle workspace
- Bob is a channels admin of the Sandcastle workspace
- Catherine and Emily are a normal members of the Sandcastle workspace
- David is a guest user
Objects of type
workspace have users related to them as:- Legacy Admin (
legacy_admin) - Channels Admin (
channels_admin) - Member (
member) - Guest (
guest)
01. Individual permissions
To keep things simple and focus on Auth0 FGA rather than Slack complexity, we will model only four roles (legacy_admin, channels_admin, member, guest). At the end of this section we want to have the following permissions represented
To represent permissions in Auth0 FGA we use relations. For workspace permissions we need to create the following authorization model:
The Auth0 Fine-Grained Authorization (FGA) service determines if a user has access to an object by checking if the user has a relation to that object. Let us examine one of those relations in detail:
The snippet above indicates that objects of type workspace have users related to them as “member” if those users belong to the userset of all users related to the workspace as “member”.This means that a user can be directly related as a member to an object of type “workspace”
amy is a legacy_admin of workspace:sandcastle we create this relationship tuple
We can now ask Auth0 FGA “is amy a legacy_admin of workspace:sandcastle?”
We can also say that catherine is a member of workspace:sandcastle:
And verify by asking Auth0 FGA
Catherine, on the other hand, is not a legacy_admin of workspace:sandcastle.
Repeat this process for the other relationships
Verification
To verify, we can issue check request to verify it is working as expected. Let’s try to verify the followings:02. Updating The workspace Authorization Model With Implied Relations
Some of the queries that you ran earlier, while returning the correct response, do not match reality. One of which is:
As you saw before, running this query will return amy is not a member of workspace:sandcastle, which is correct based on the data you have given Auth0 Fine-Grained Authorization (FGA) so far. But in reality, Amy, who is a legacy_admin already has an implied channels_admin and member relations. In fact anyone (other than a guest) is a member of the workspace.
To change this behavior, we will update our system with a concentric relationship model.
With the following updated authorization model, you are informing Auth0 Fine-Grained Authorization (FGA) that any user who is related to a workspace as legacy_admin, is also related as a channels_admin and a member .
We can then verify amy is a member of workspace:sandcastle.
We can check for other users and relationships.
03. Updating the authorization model to include channels
So far, you have modeled the users’ relations to the workspace itself. In this task you will expand the model to include the relations concerning the channels. By the end of it, you will run some queries to check whether a user can view or write to a certain channel. Queries such as:is david related to channel:general as viewer?(expected answer: No relation, as David is a guest user with only a relation to #proj-marketing-campaign)is david related to channel:proj_marketing_campaign as viewer?(expected answer: There is a relation, as there is a relation between David and #proj-marketing-campaign as a writer)is bob related to channel:general as viewer?(expected answer: There is a relation, as Bob is a member of the Sandcastle workspace, and all members of the workspace have a viewer relation to #general)
- Amy, Bob, Catherine and Emily, are normal members of the Sandcastle workspace, they can view all public channels, in this case: #general and #proj-marketing-campaign
- David, a guest user, has only view and write access to the #proj-marketing-campaign channel
- Bob and Emily are the only ones with either view or write access to the #marketing-internal channel
- Amy and Emily are the only ones with write access to the #general channel
- Workspace includes the channel, consider the relation that of a parent workspace
- A user can be a viewer and/or writer on a channel
The configuration snippet above describes a channel that can have the following relations:
- workspaces related to it as
parent_workspace - users related to it as
writer - users related to it as
viewer
Implied relation
There is an implied relation that anyone who can write to a channel can also read from it, so the authorization model can be modified to be:Note that the channel type definition has been updated to indicate that viewer is the union of:
- the set of users with a direct viewer relation to this object
- the set of users with writer relations to this object
Updating relationship tuples
What remains is to add the relationship tuples to indicate the relation between the users, workspace and the channels. The Sandcastle workspace is a parent workspace of the #general, #marketing-internal and #proj-marketing-campaign channels.#general channel
The #general channel is a public channel visible to all the members of the workspace. In Auth0 FGA, you represent this relation in the form of the following relationship tuple:
This indicates The set of users related to
workspace:sandcastle as member are also related to channel:general as viewer#marketing-internal channel
The #marketing-internal is visible to only Bob and Emily. They can view and write in it.
#proj-marketing-campaign channel
The #proj-marketing-campaign is public to all members of the Sandcastle workspace. They can view and write in it.
David is a guest user who can also view and write to #proj-marketing-campaign
Verification
Now that you have added the necessary relationship tuples, you will check to make sure that your configuration is valid. First, we want to ensure david is not related to channel:general as viewer. David should be related to channel:proj_marketing_campaign as viewer. Repeat this for the following relationsSummary
- Have a basic understanding of authorization and Auth0 FGA Concepts.
- Understand how to model authorization for a communication platform like Slack using Auth0 FGA.
- were introduced to fine-grained authentication and Auth0 FGA.
- learned how to build and test an Auth0 Fine-Grained Authorization (FGA) authorization model for a communication platforms like Slack.
Exercises for you
- Try adding more relationship tuples to represent other users and channels being added. Then run queries to make sure that the authorization model remains valid.
- Update the configuration to model more Slack permissions (workspace owners, Slack orgs), then add the relationship tuples necessary and run some queries to validate your configuration.