

Before you start
Before you start this guide, make sure you’re familiar with some Auth0 FGA Concepts and know how to develop the things listed below.Step By Step
Starting with the authorization model mentioned above, we want to enable users to create their own custom roles, and tie permissions to those roles to our two users and to the permissions on the logo asset category. For this guide, we’ll model a scenario where a certain organization using our app has created anasset-category called “logos”, and another called “text content”.
The company administrator would like to create:
- a media-manager role that allows users to edit assets in the logos asset category
- a media-viewer role that allows users to view all assets in the logos asset category
- a blog-editor role that allows users to edit all assets in the text content asset category
- a blog-viewer role that allows users to view all assets in the text content asset category
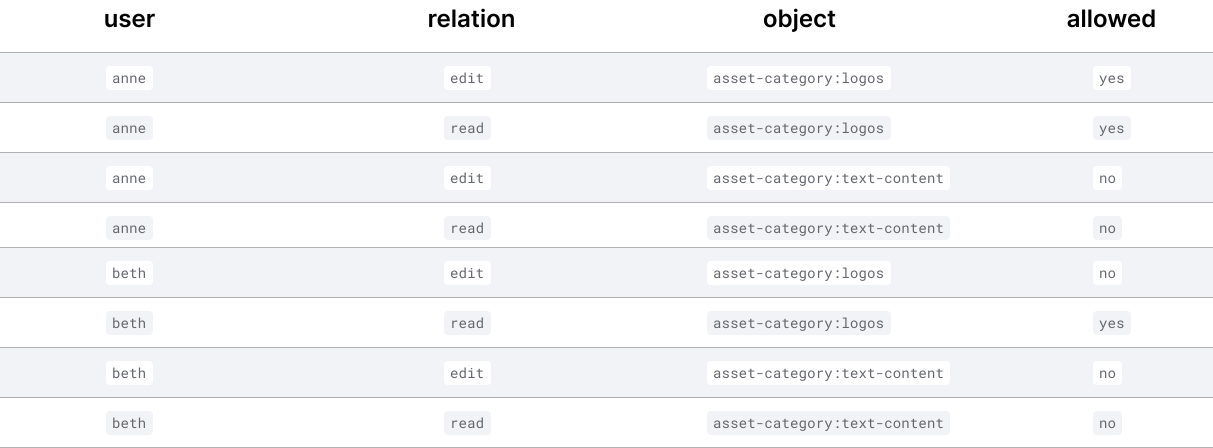
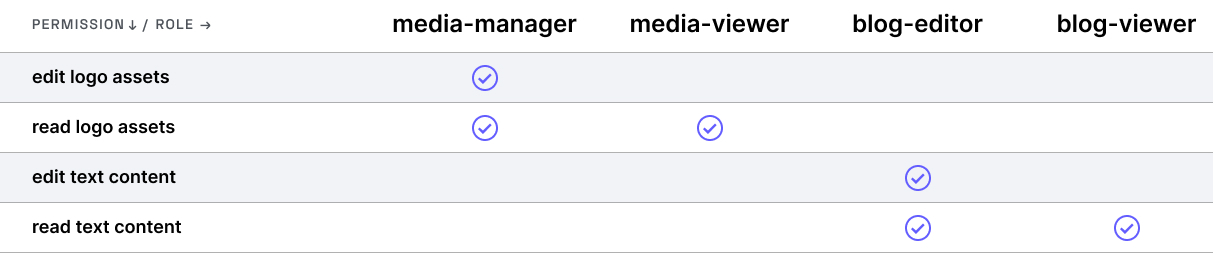 Finally, the administrator wants to assign Anne the media-manager role and Beth the media-viewer role.
At the end, we’ll verify our model by ensuring the following access check requests return the expected result.
 In order to do this, we need to:
- Update the Authorization Model to add a Role Type
- Use Relationship Tuples to tie the Users to the Roles
- Use Relationship Tuples to associate Permissions with the Roles
- Verify that the Authorization Model works
01. Update The Authorization Model To Add A Role Type
Because our roles are going to be dynamic and might change frequently, we represent them in a new type instead of as relations on that same type. We’ll create new type calledrole, where users can be related as assignee to it.
The authorization model becomes this:
With this change we can add relationship tuples indicating that a certain user is assigned a certain role.
02.Use Relationship Tuples To Tie The Users To The Roles
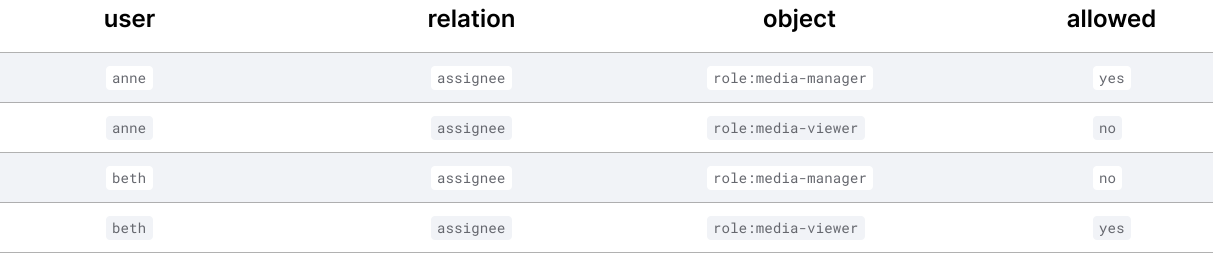
Once we’ve added therole type, we can assign roles to Anne and Beth. Anne is assigned the “media-manager” role and Beth is assigned the “media-viewer” role. We can do that by adding relationship tuples as follows:
We can verify they are members of said roles by issuing the following check requests:
03. Use Relationship Tuples To Associate Permissions With The Roles
With our users and roles set up, we still need to tie members of a certain role to it’s corresponding permission(s).04. Verify That The Authorization Model Works
To ensure our model works, it needs to match our expectations:
The checks come back as we expect, so our model is working correctly.